Exaforce Wants to Reinvent the SOC With Agentic AI
Security operations centers (SOCs) are drowning in data, and most “AI-powered” tools do little more than help junior analysts sort through alerts. Exaforce is betting big on a broader vision.
Security operations centers (SOCs) are drowning in data, and most “AI-powered” tools do little more than help junior analysts sort through alerts. Exaforce is betting big on a broader vision.
San Francisco, August 2025 – Wallarm, the unified platform for API and agentic AI security, today released its Q2 2025 API ThreatStats Report, revealing significant shifts in the API threat landscape. The report highlights a steep rise in logic-layer vulnerabilities and a new wave of exploits targeting AI development and orchestration environments.
As companies rush to embed large language models (LLMs) into their apps, one nagging problem keeps surfacing: what happens when sensitive data sneaks into AI prompts, logs, or SDK integrations?
ActiveFence, the self-described “AI Safety” company, has published its first AI Security Benchmark Report: Prompt Injections, and the results put its model at the top of the pack.
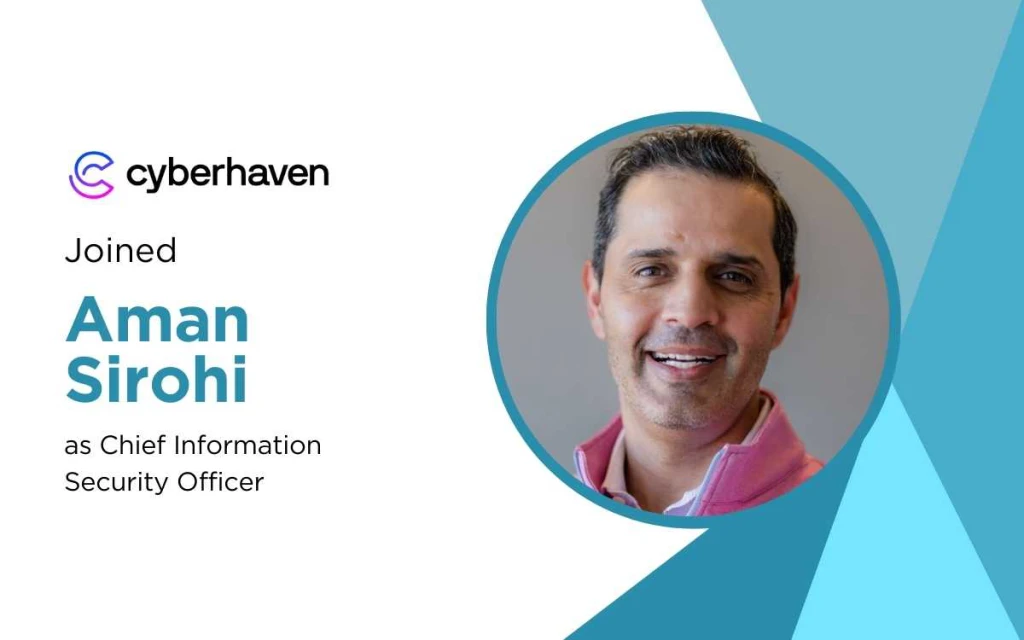
Cyberhaven is adding serious firepower to its leadership team. The AI-powered data security company has appointed Aman Sirohi as Chief Information Security Officer (CISO), tapping a veteran with more than 20 years of experience in cybersecurity, risk management, and data protection.
The U.S. government’s cloud modernization drive just got a new player. Knox Systems today announced it has achieved FedRAMP High authorization, one of the most stringent federal security certifications available. The milestone clears the way for commercial SaaS and AI platforms running on the Knox Cloud to serve federal agencies—potentially in as little as 90 days.
Your organization is during a product launch. The marketing campaigns are live, and your operations are running at full capacity. But then a cyberattack hits. Customer data is locked behind ransomware, and your team tries to contain the breach. The question is whether you can maintain operational continuity. This is where cyber resilience comes…
Multi-factor authentication (MFA), once hailed as a security panacea, is proving increasingly vulnerable. In 2024, a staggering 87% of successful cyberattacks exploited session hijacking post-MFA login, exposing a critical flaw: MFA trusts session tokens blindly. State-sponsored threat groups like Russia’s Void Blizzard use sophisticated proxy tools such as Evilginx2 to steal tokens in real time—leaving security teams in the dark.
As autonomous systems spread from factory floors to farmland, the demand for smarter, safer control is rising—and FORT Robotics is cashing in on it